Solvere Organisation Security brings scanning, risk assessment, a vendor portal, digital signatures and auditable governance into one platform — built for organisations with strict demands on traceability, data control and compliance.
Vendor data, assessments, evidence and decisions live in spreadsheets, inboxes and separate tools. When the landscape changes faster than the review cycle, exposure slips through unnoticed — while NIS2, DORA and audit expectations keep rising.
Manual vendor review takes weeks — the risk picture can change several times in the meantime.
Without a unified log and signed decisions, supervisory and internal audit questions are hard to answer.
Every exposed vendor service can become a way in — and most have more than they think.
NIS2, DORA and sector requirements point to continuous third-party control — annual sampling is no longer enough.
See how Solvere Organisation Security supports the operational flow, assessments and collaboration, and access and governance.
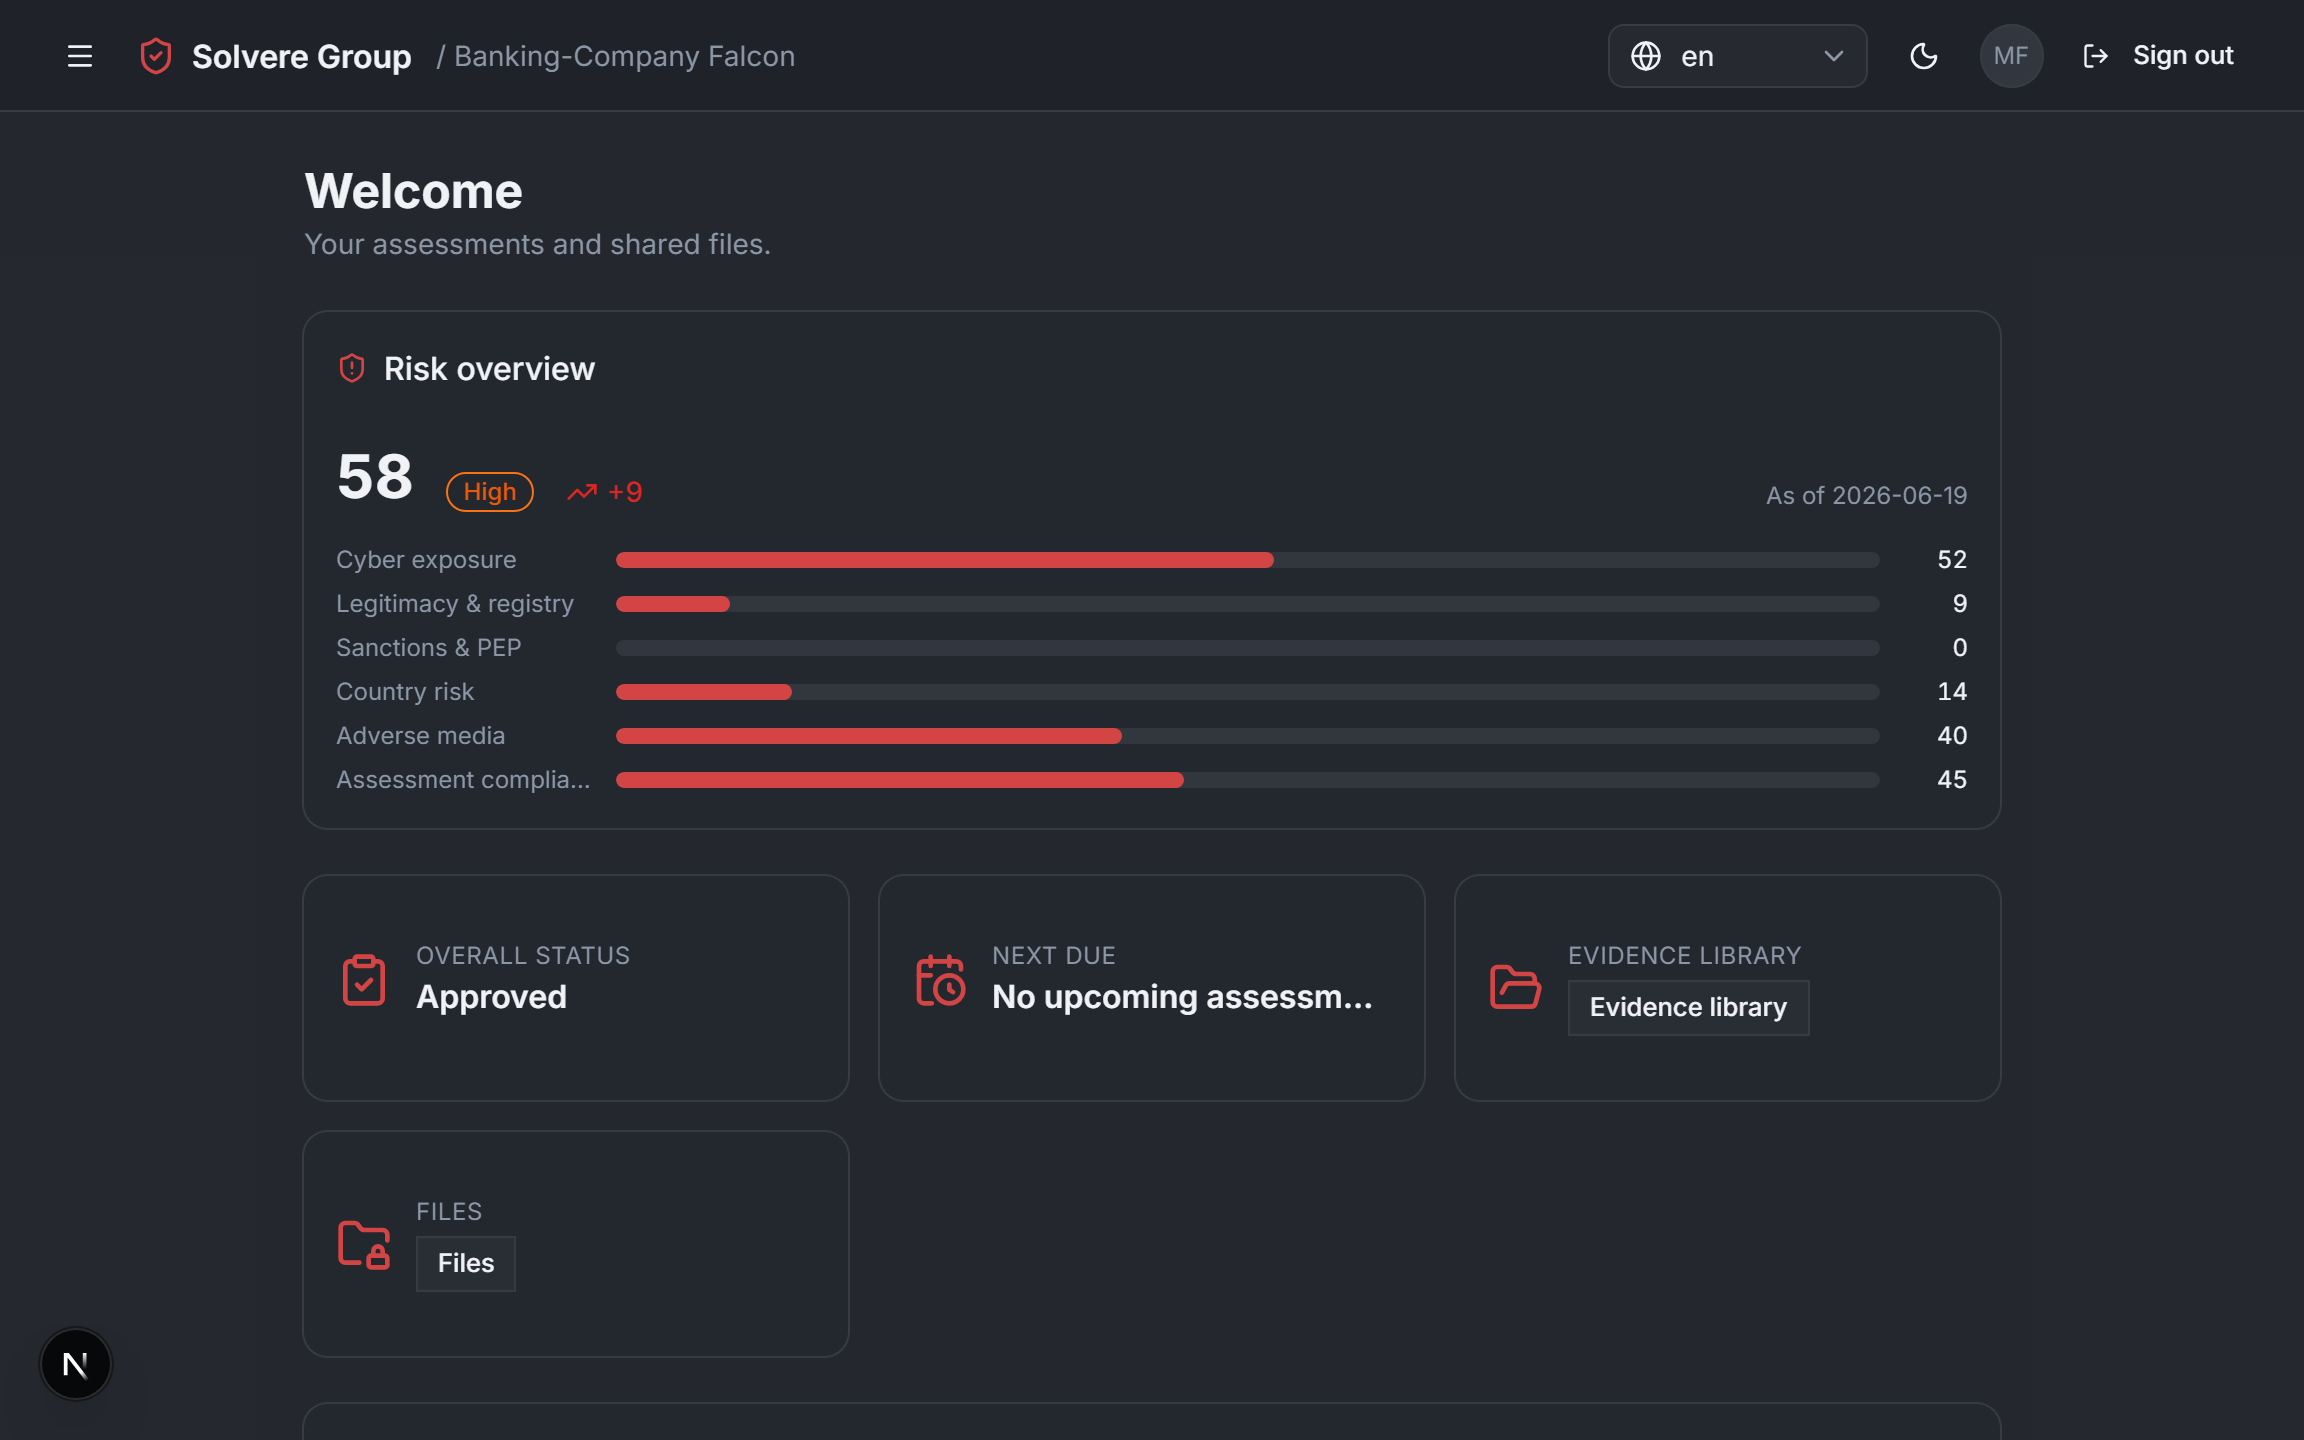
Invite vendors into their own scoped portal where they answer assessments, upload evidence and sign — all fed back to your risk hub in real time.
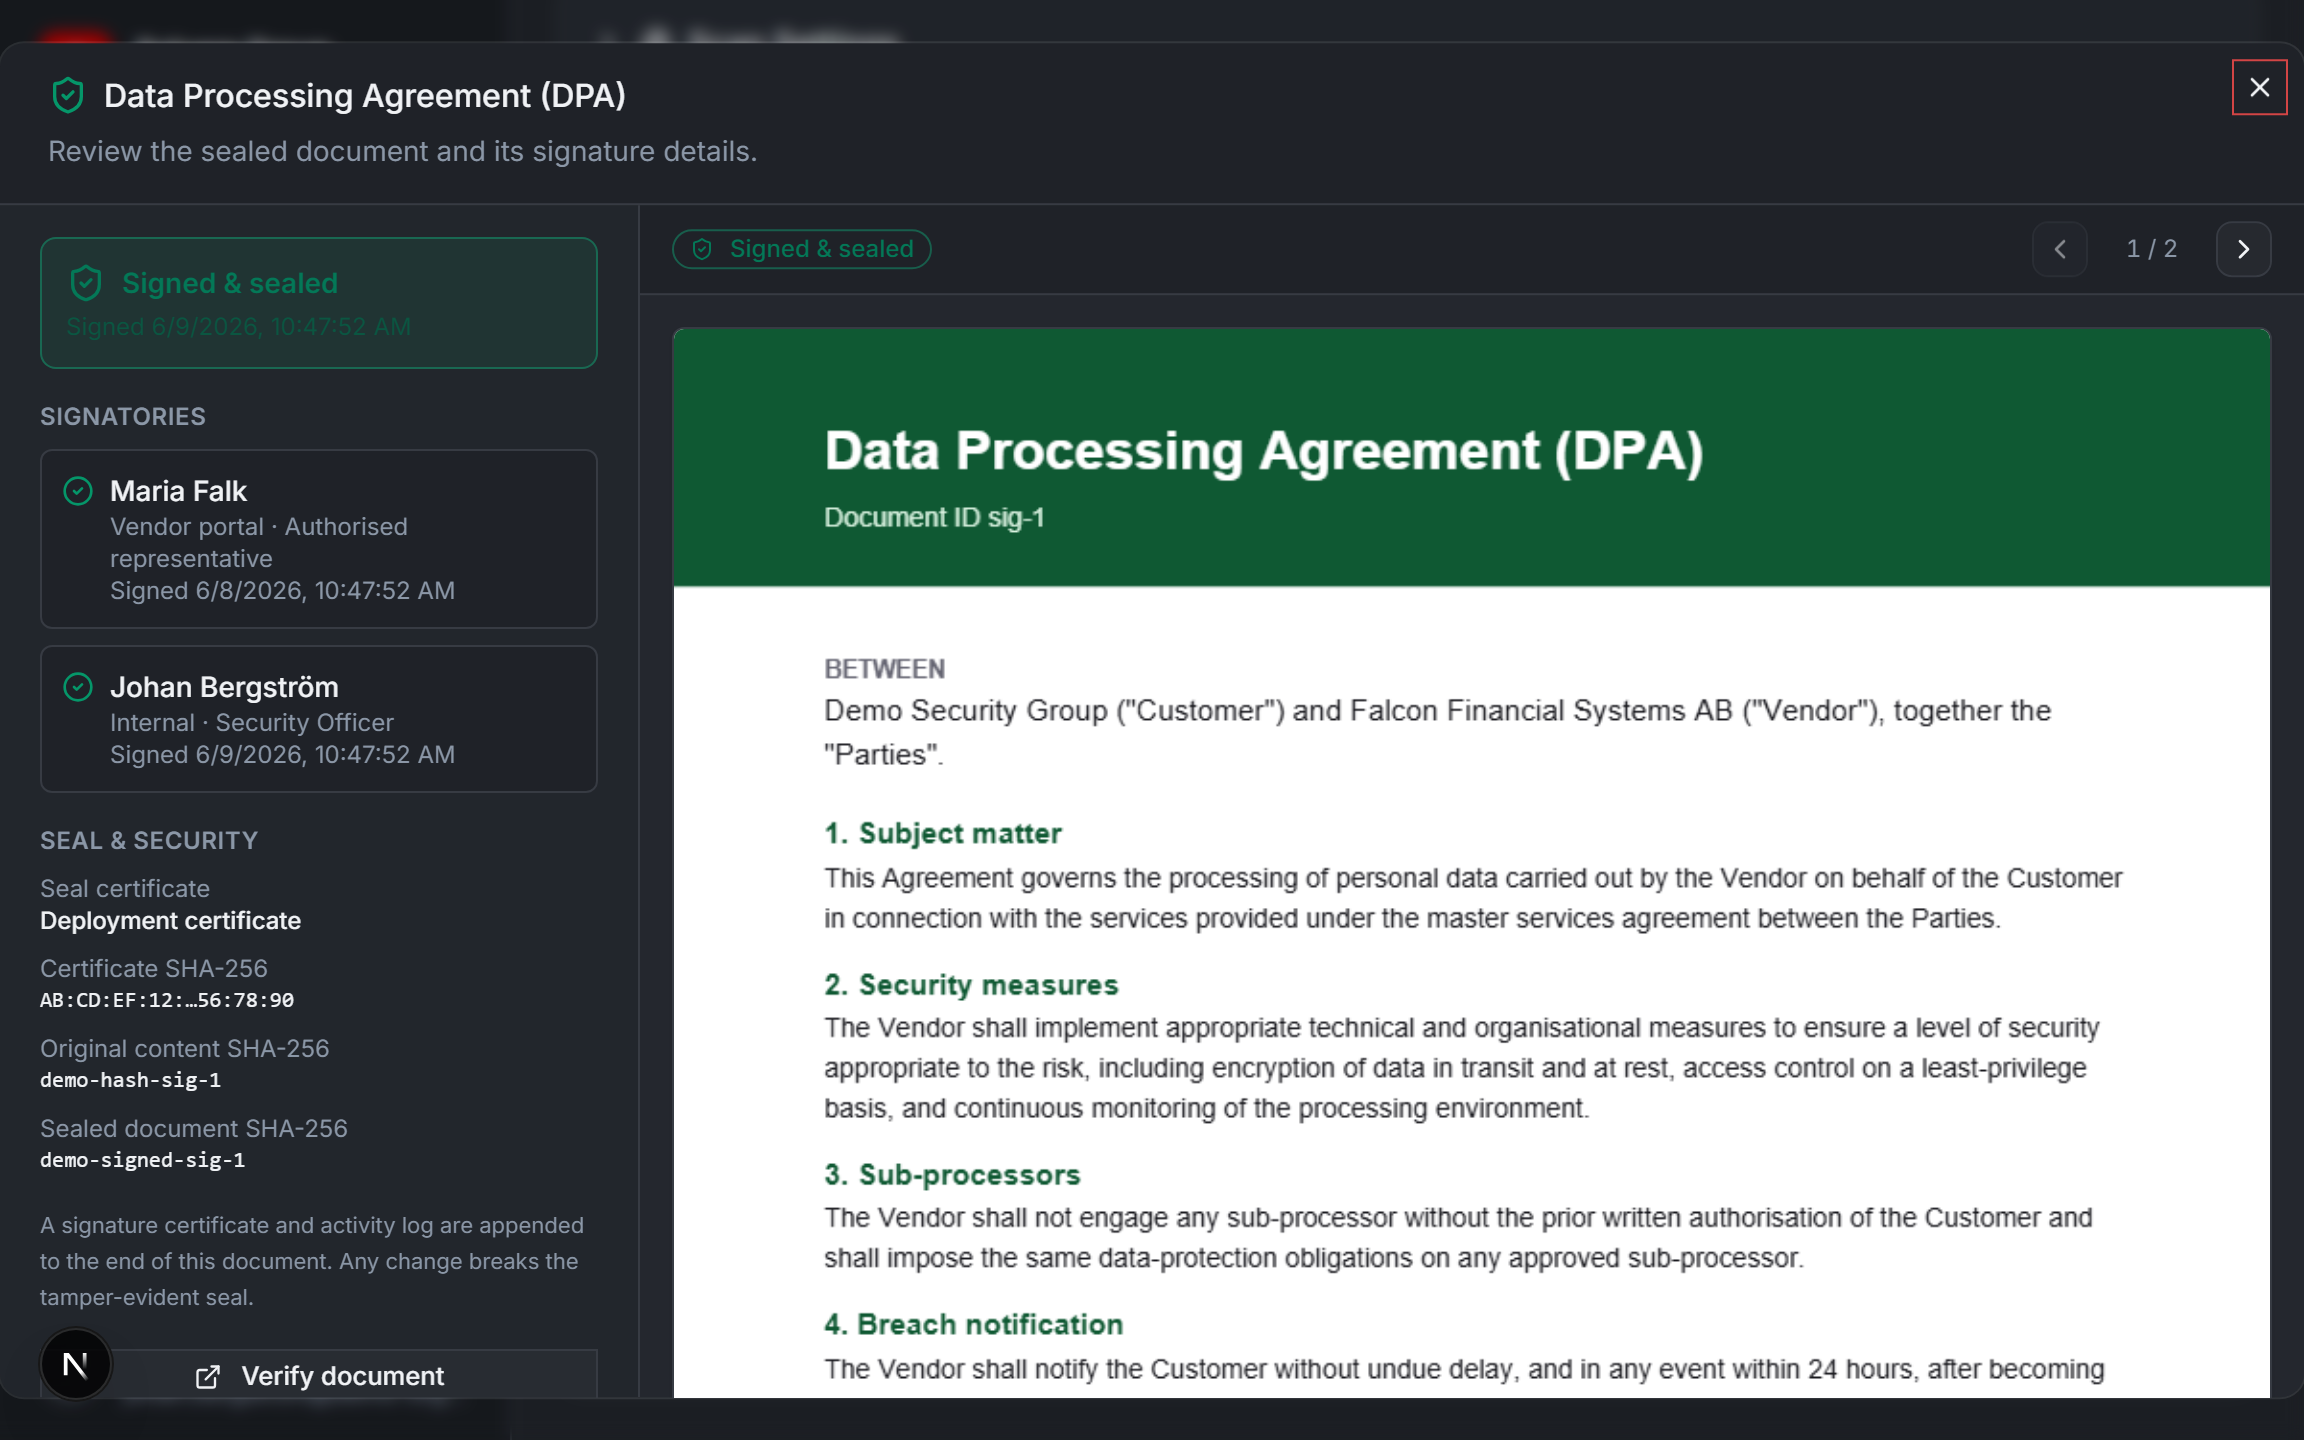
Assessments and decisions can be signed digitally and sealed into traceable PDF documents. Every signature is bound to identity, time and content — verifiable after the fact.
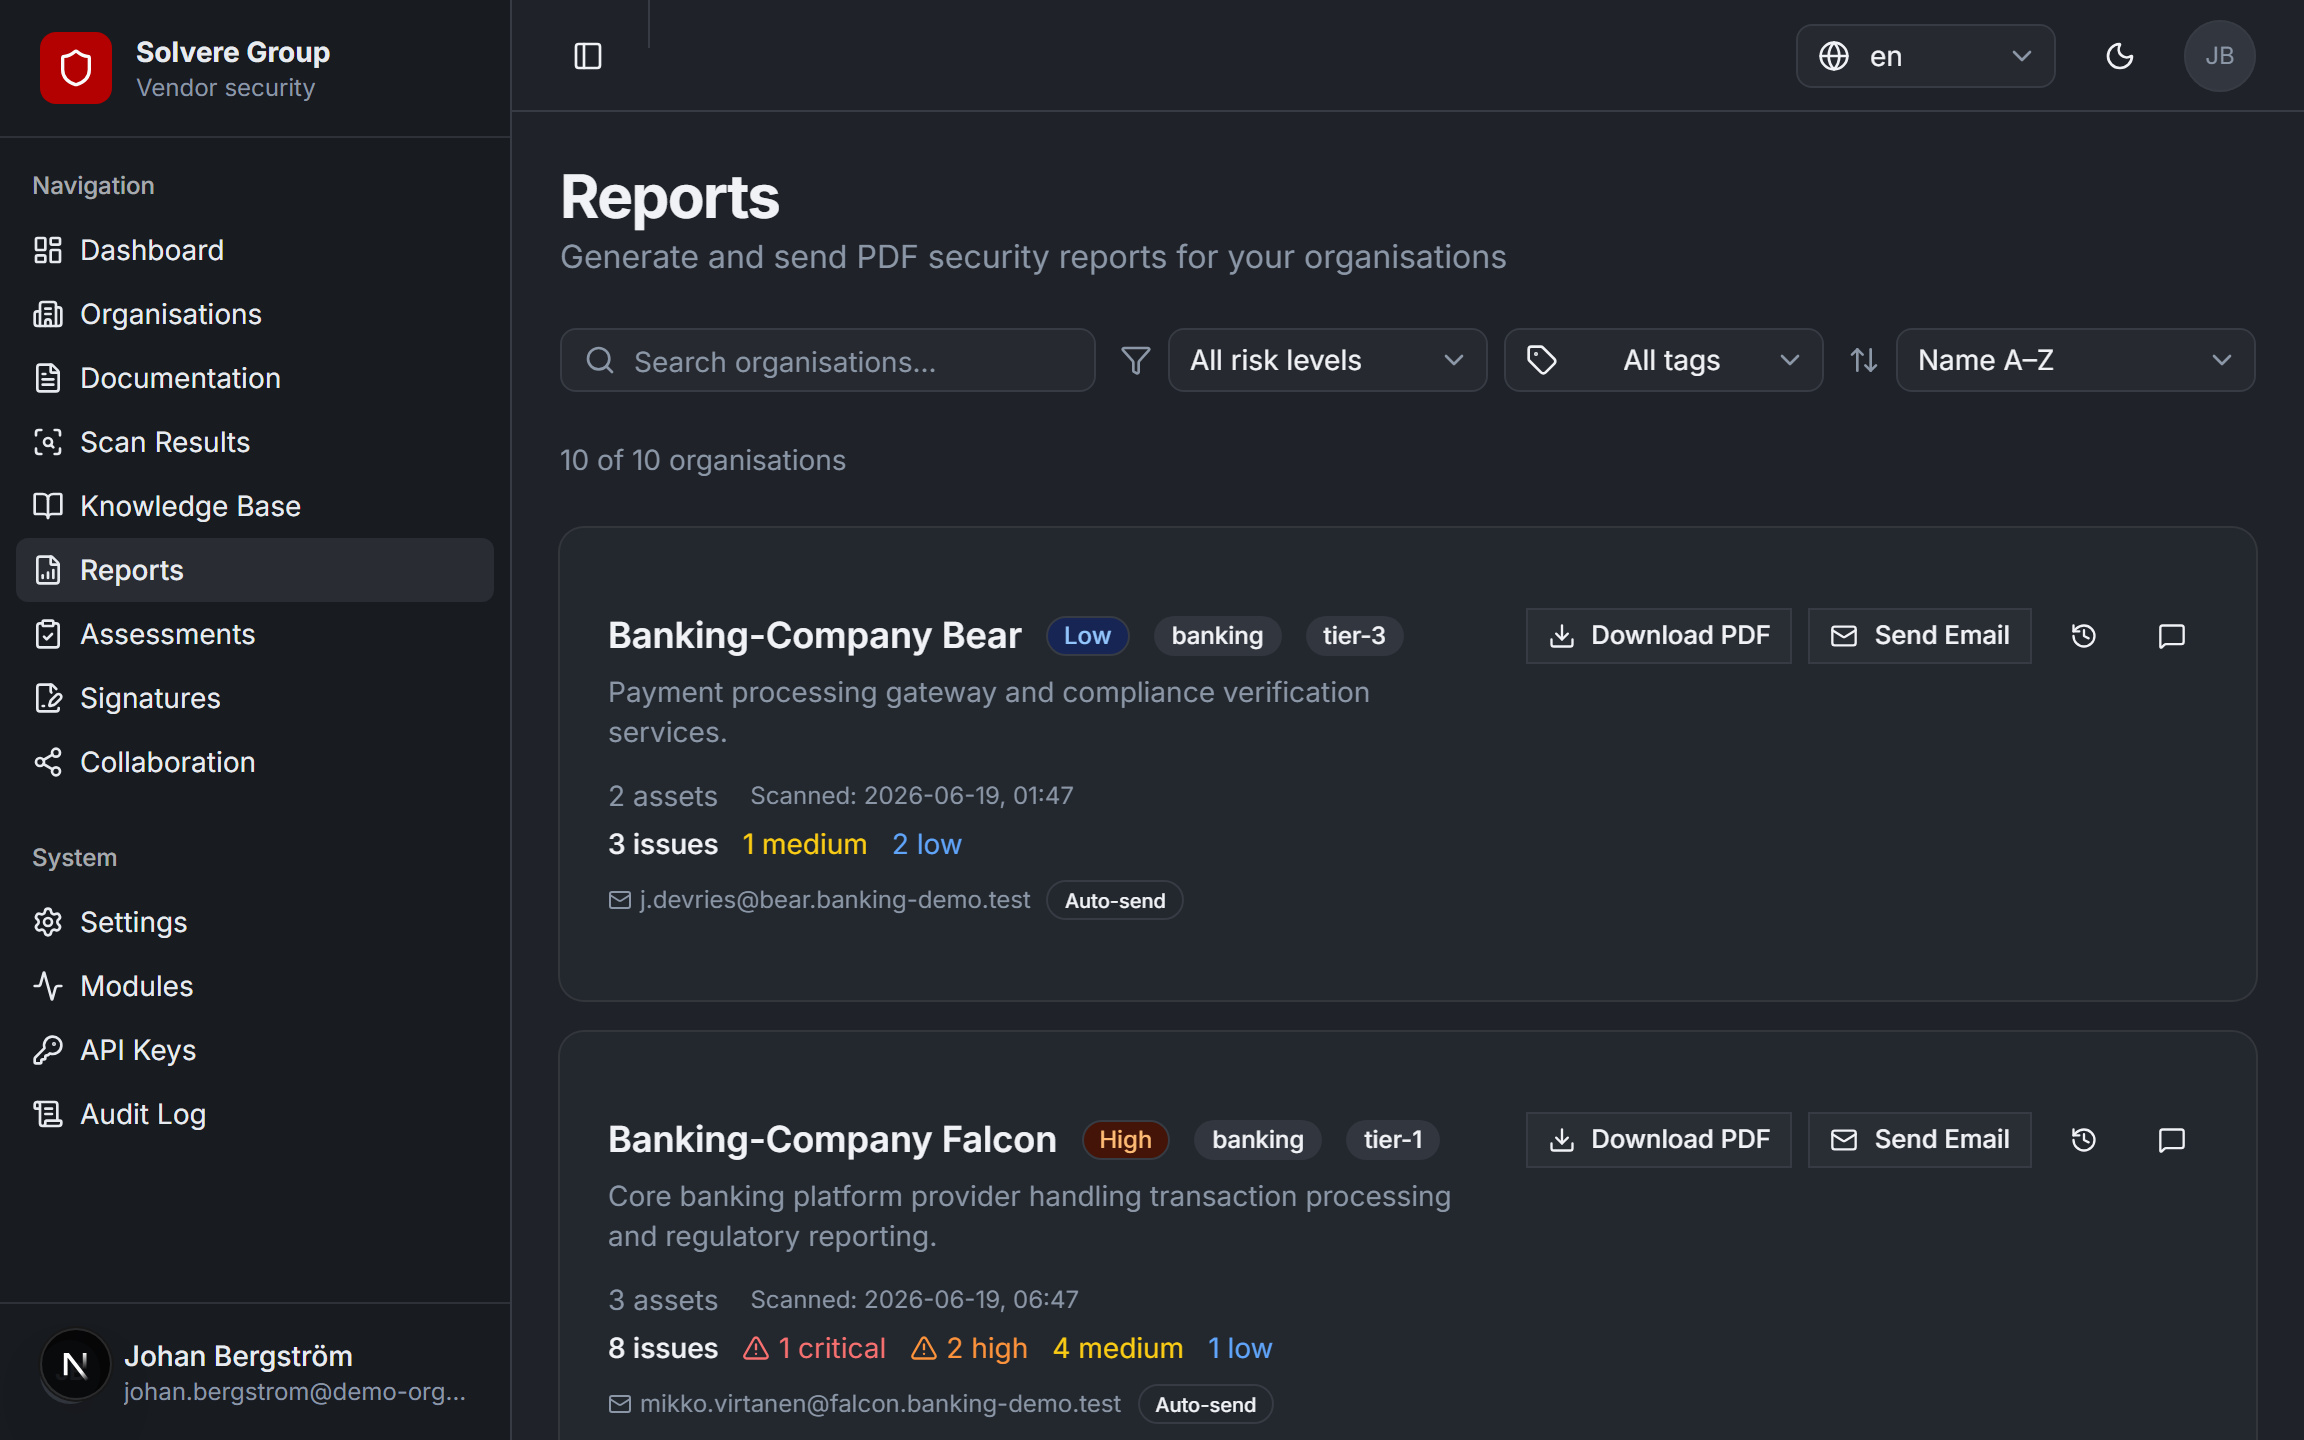
Schedule and deliver recurring reports per vendor — right language, right recipient, right time. Backed by a structured knowledge base and documentation.
Continuously scan your vendors' external attack surface — DNS, TLS, headers, ports and subdomains.
Structured assessments where the vendor answers, uploads evidence and is followed up in the portal.
Sign and seal decisions into auditable PDF documents bound to identity and timestamp.
Deployed inside your own infrastructure via Docker. No external data transfer — built for sensitive environments.
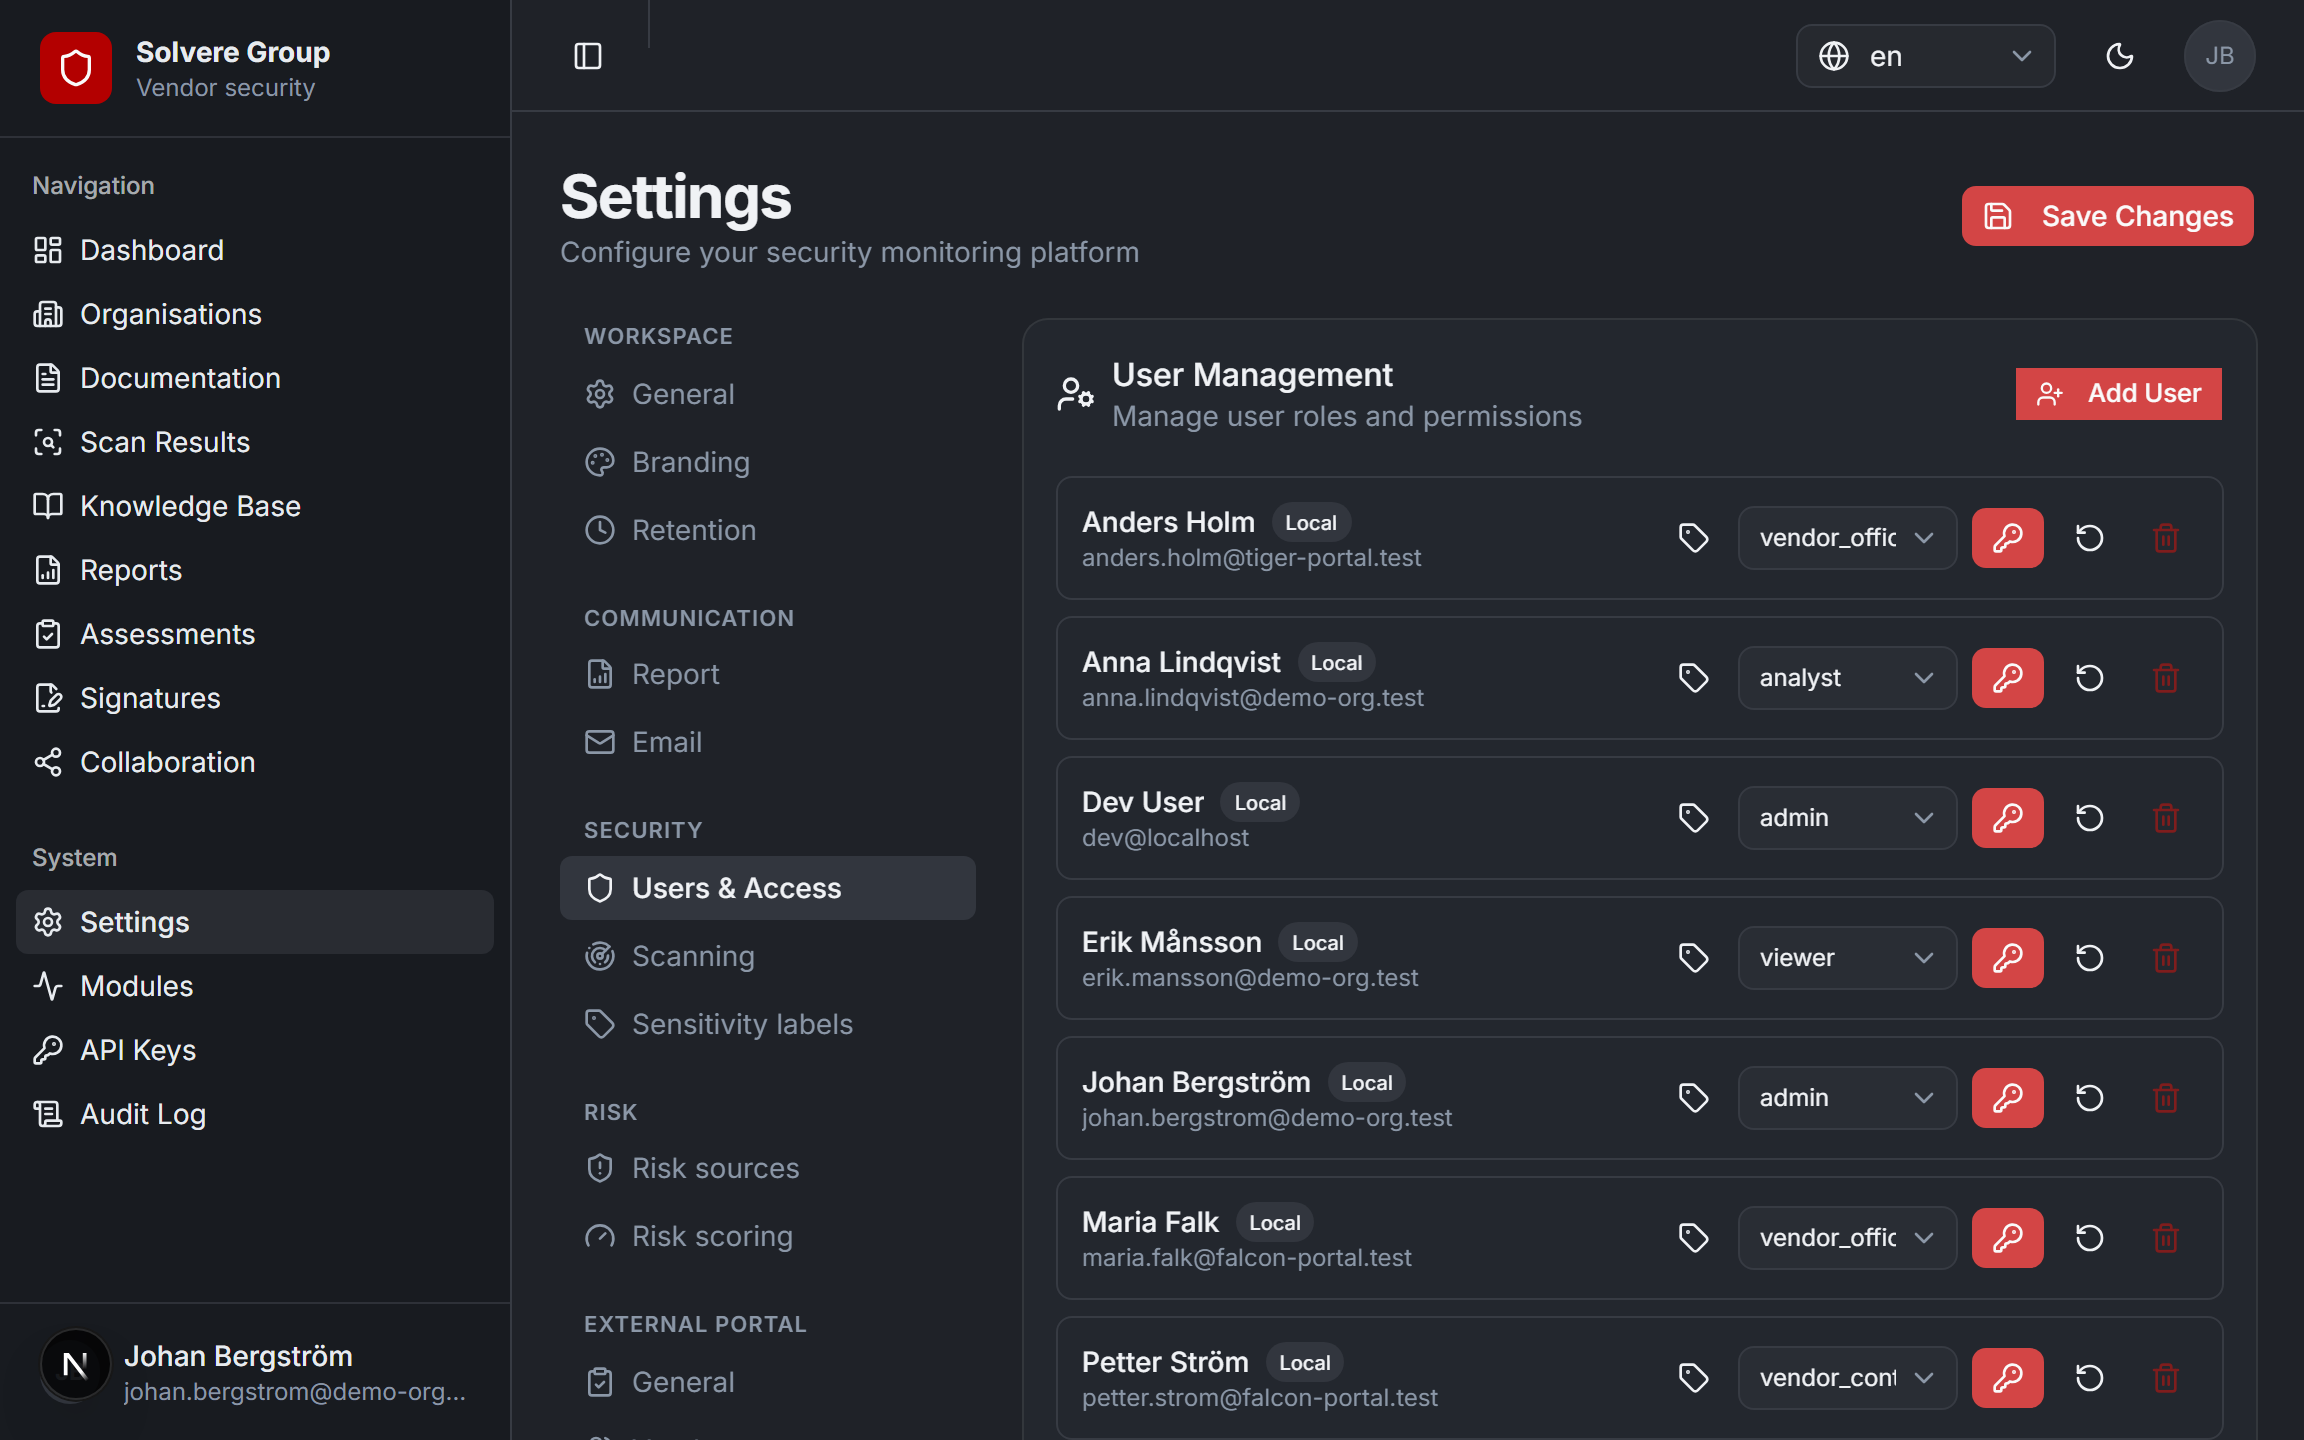
Fine-grained access, identity integration and complete traceability — configurable per organisation and module.
SSO and app roles via Microsoft Entra ID, or local user management — role-based access end to end.
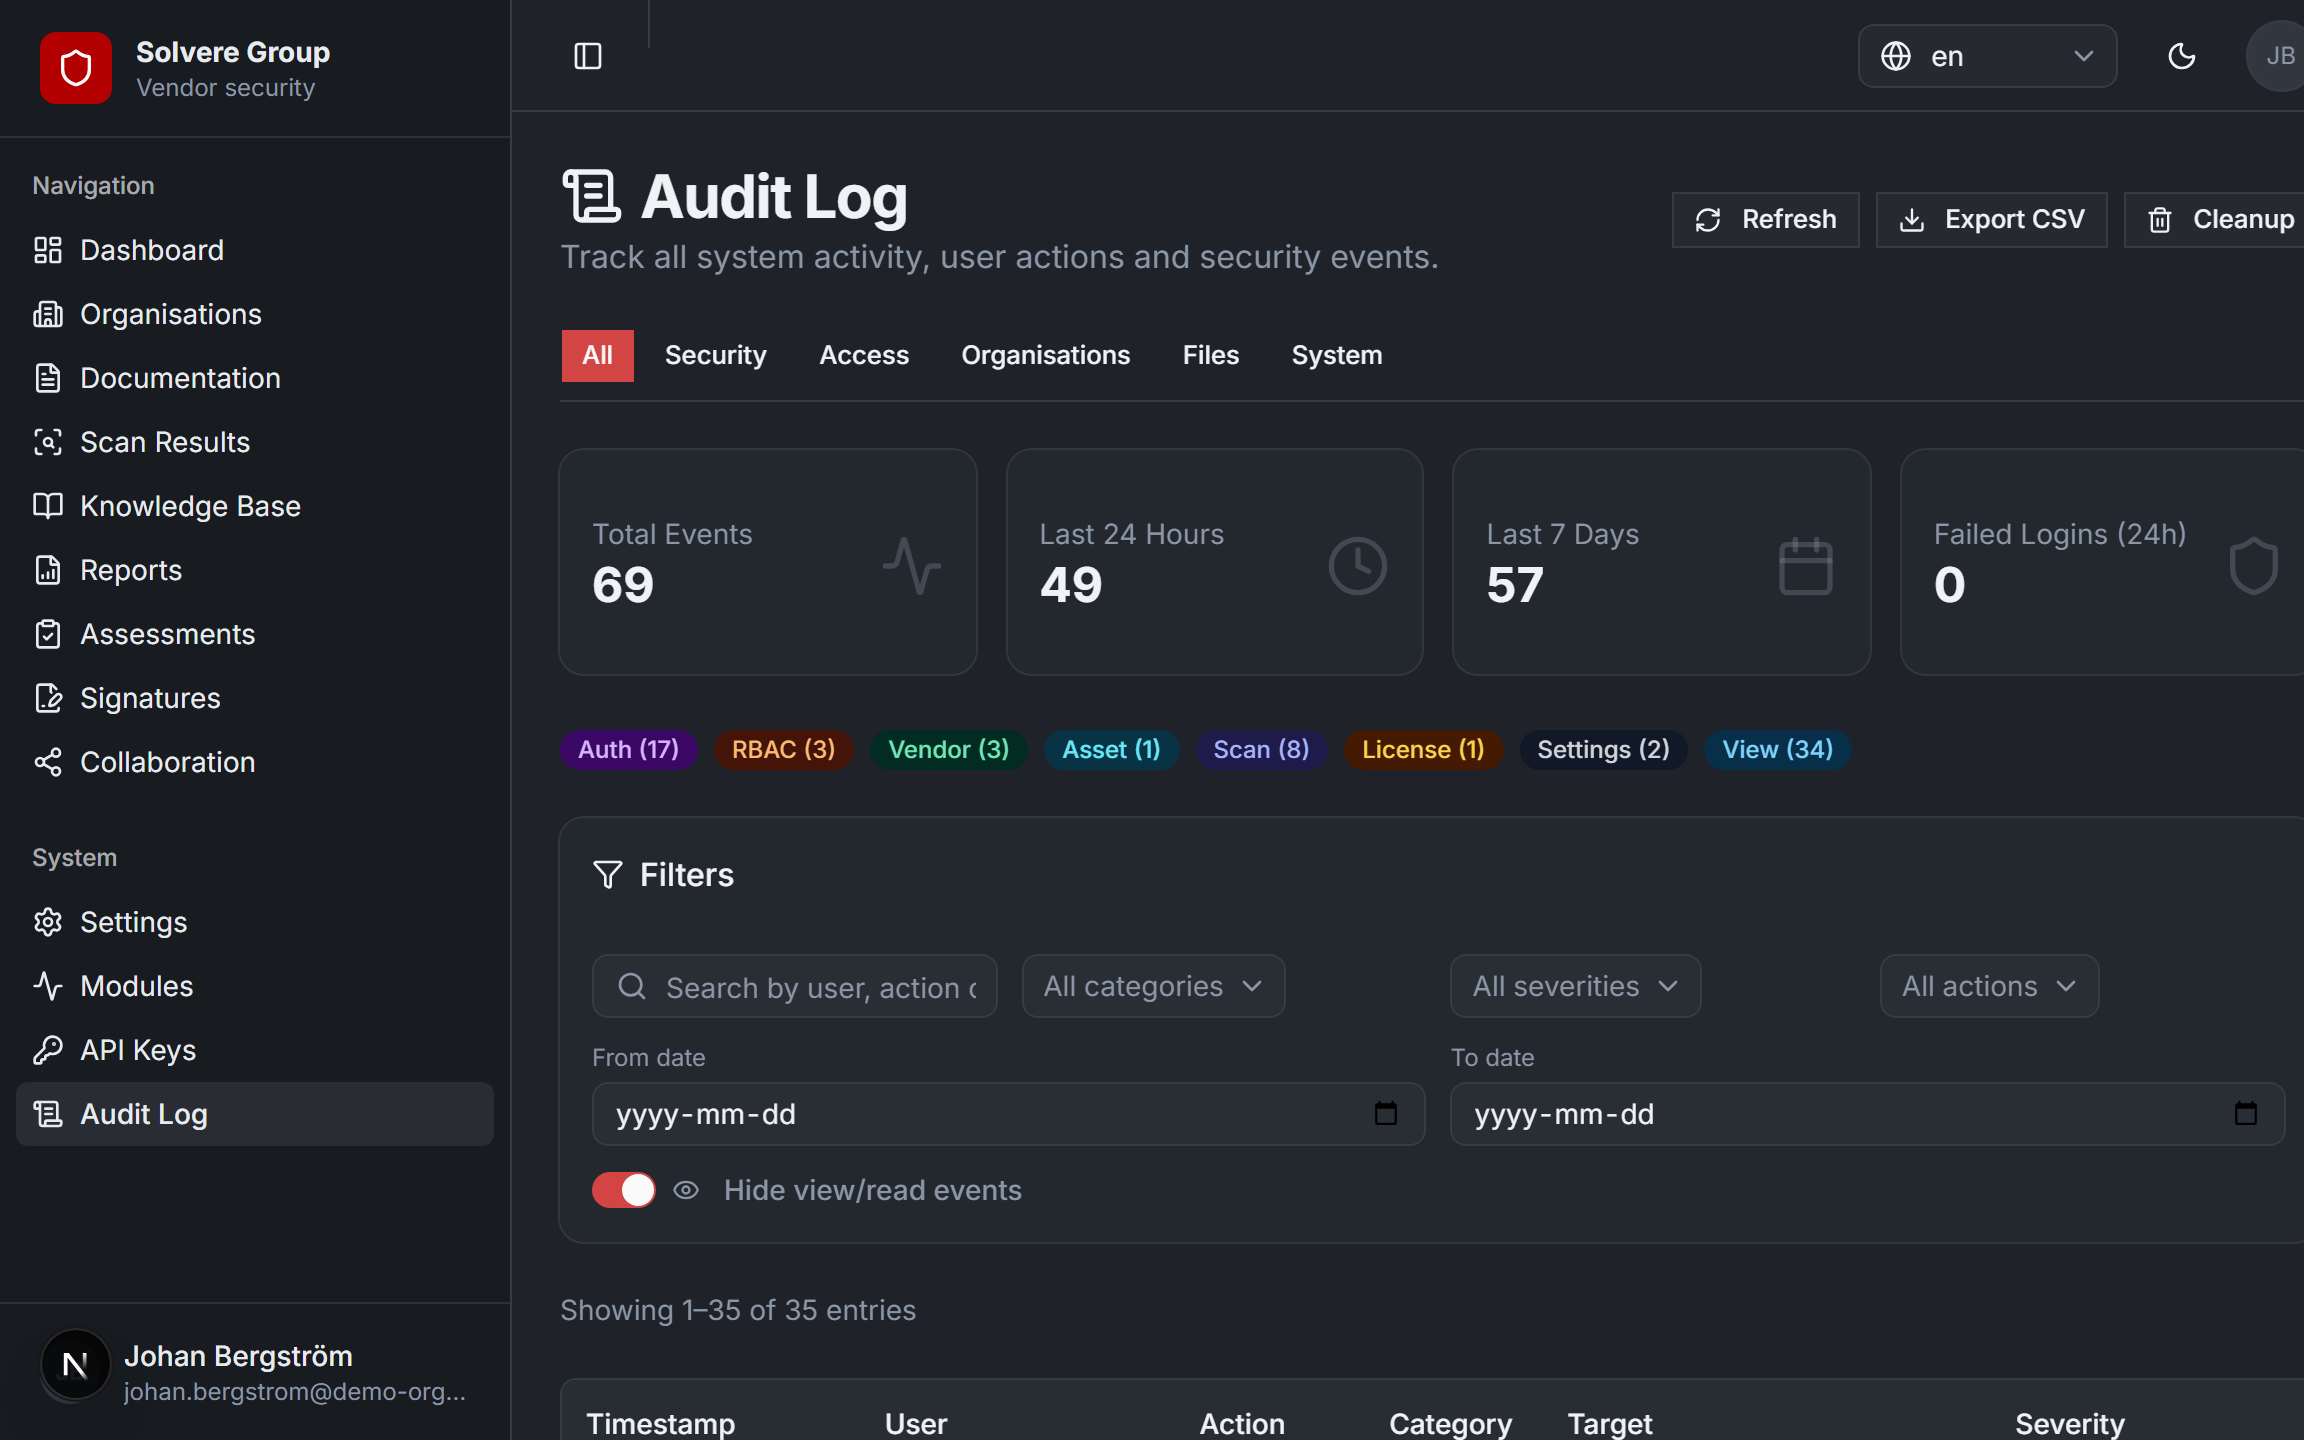
Full traceability for every critical activity — who did what and when, in one unbroken chain.
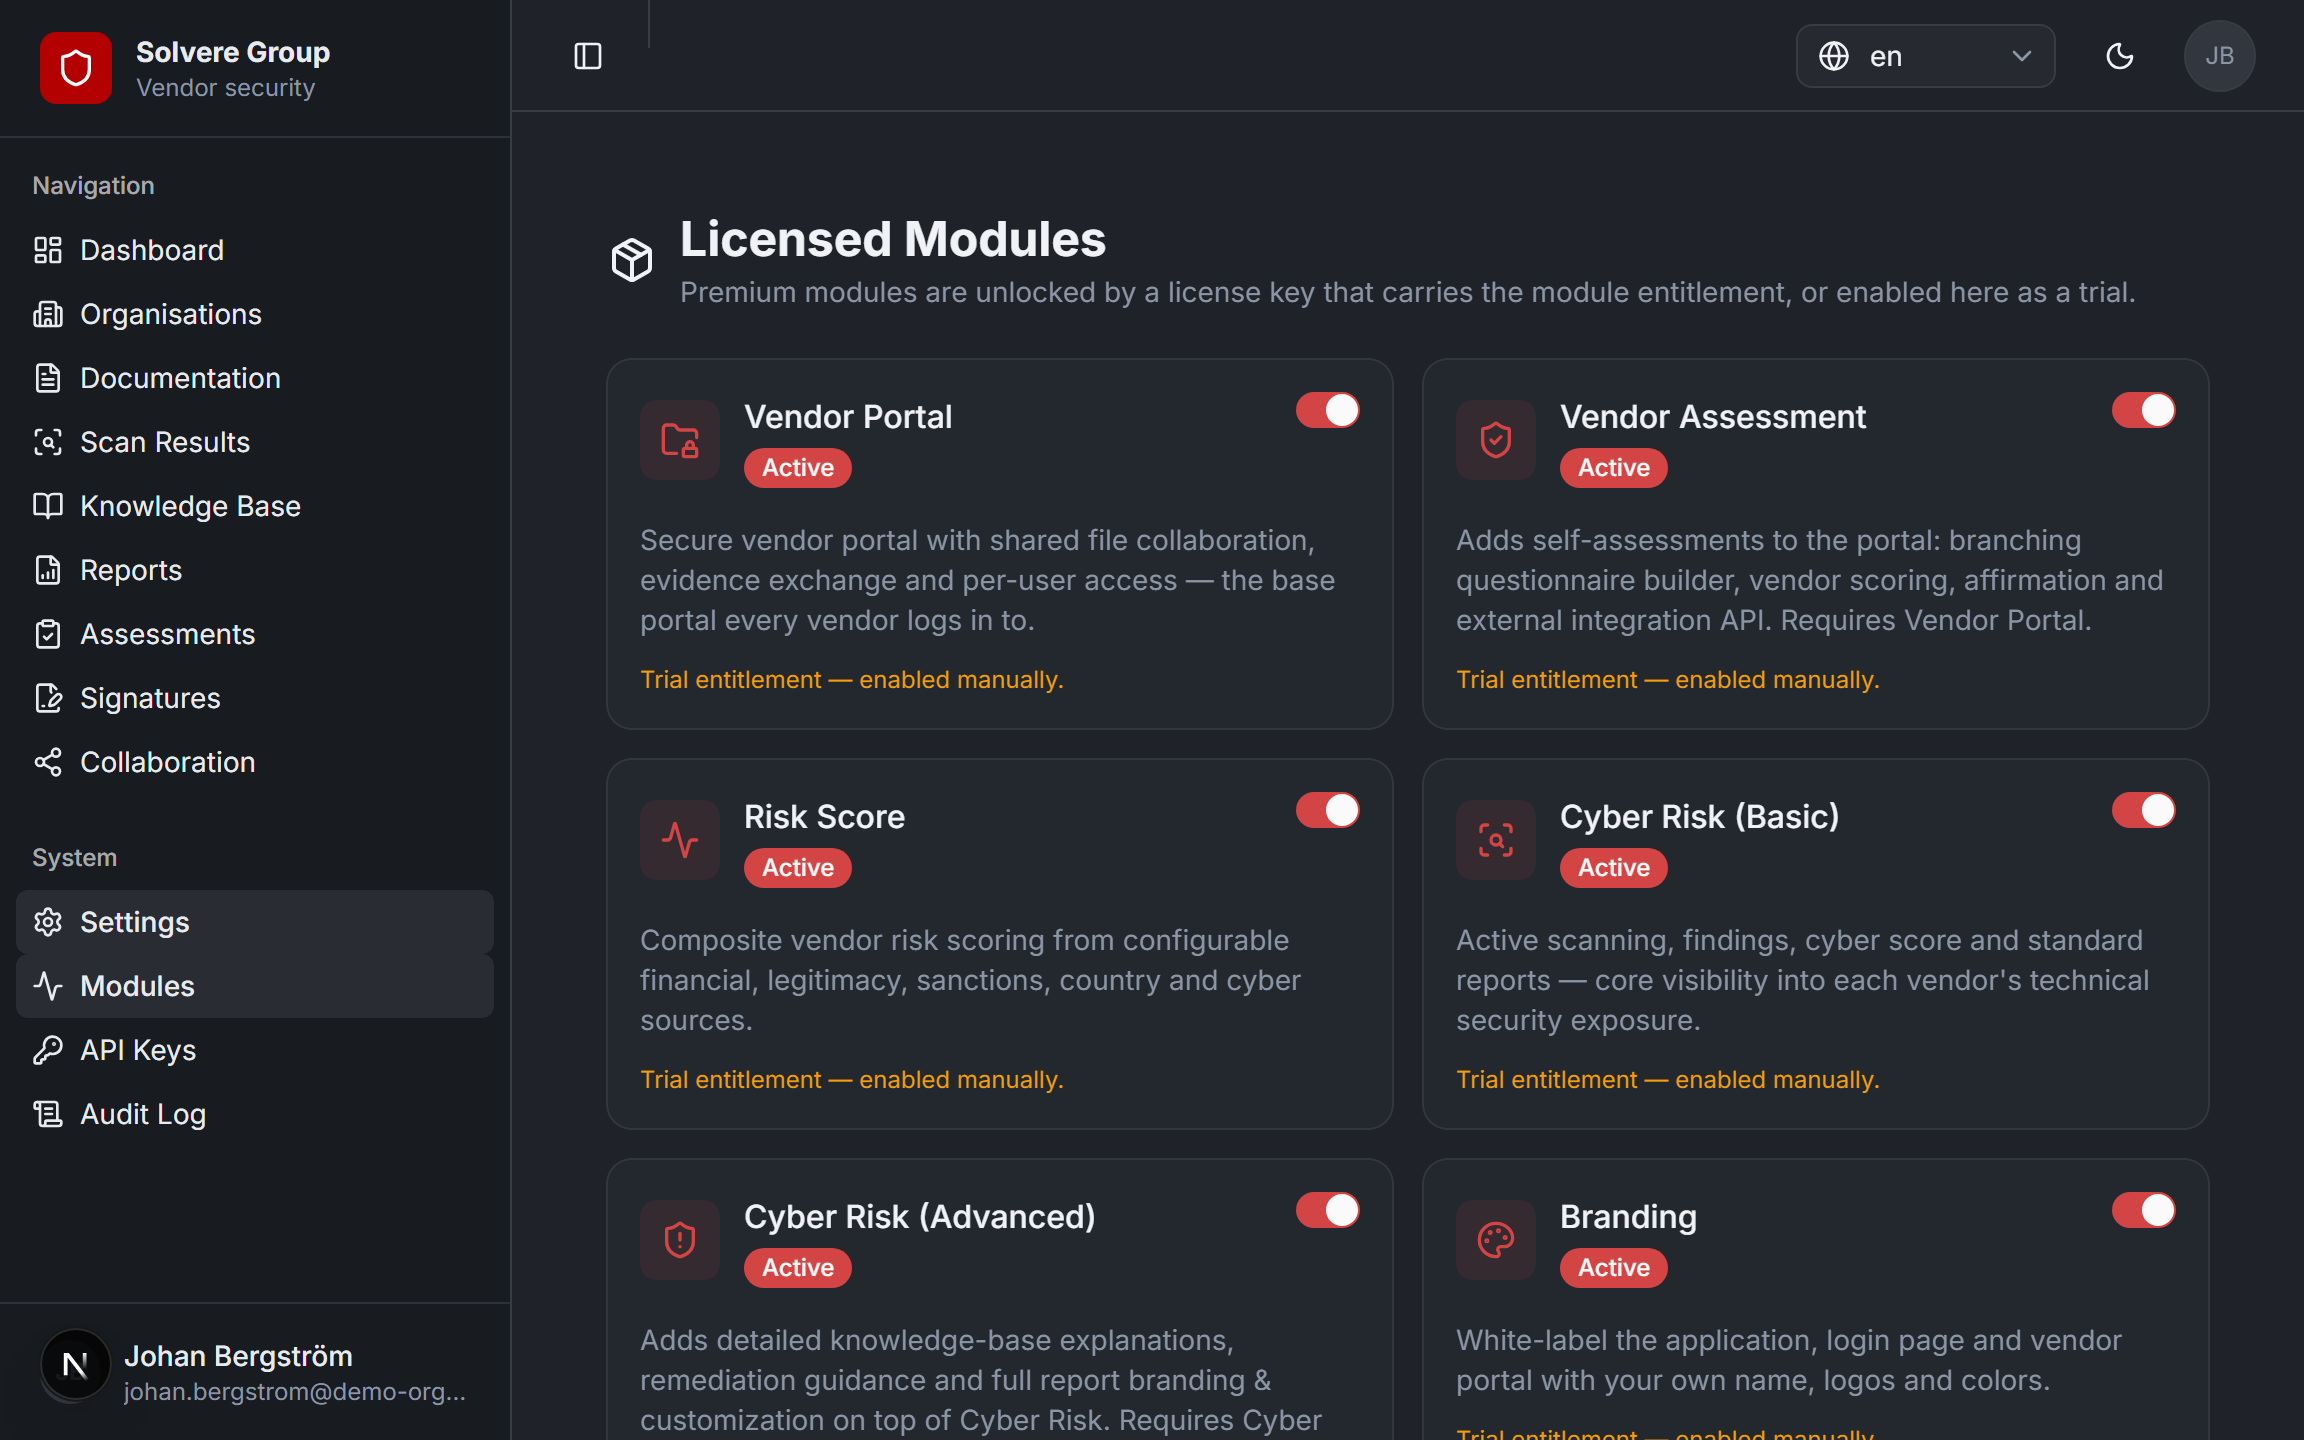
Enable capabilities as needed and classify data by sensitivity — shape the platform around your governance model.
Configurable risk scoring and API keys for integration with your existing systems.
| Capability | Manual process | Generic tools | Solvere Organisation Security |
|---|---|---|---|
| Continuous scanning | ✗ | Limited | ✓ scheduled and automatic |
| Vendor self-service portal | ✗ | Rarely | ✓ scoped per organisation |
| Structured assessments | Spreadsheets | Varies | ✓ with evidence submission |
| Digital signing and sealing | ✗ | Separate tool | ✓ built in with traceability |
| On-prem deployment | Not applicable | Rarely | ✓ Docker-based |
| Entra ID integration | ✗ | ✗ | ✓ SSO and role provisioning |
| Automated report delivery | ✗ | Generic | ✓ Per vendor, schedule and language |
| RBAC and audit log | ✗ | Varies | ✓ Complete |
| Multilingual interface | ✗ | Rarely | ✓ English and Swedish |
The core platform is always included — vendor portal, RBAC, Entra ID SSO and audit log. Pick a bundle, capacity, deployment model, service level and contract term and see an estimated monthly cost instantly.
Vendor portal · RBAC · Entra ID SSO · Audit log · up to 25 assets.
Or toggle modules freely below — pricing updates instantly.
*Requires SSH access for installation, updates and monitoring. Without such access, operations run via VDI or co-operation via screen sharing.
Book a walkthrough with procurement and compliance — we will show how Solvere Organisation Security fits your governance model.